go high level login: Step-by-Step Access Guide for Agencies
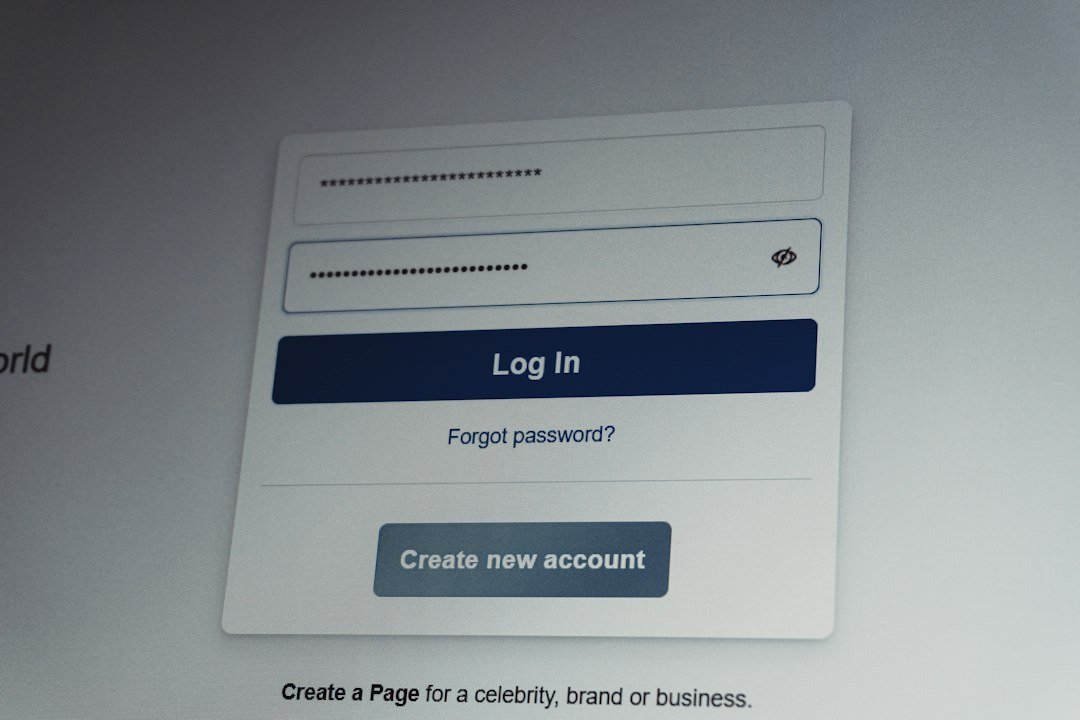
go high level login is the gateway to the HighLevel SaaS platform that agencies use for CRM, funnels, and automated marketing. To get in, open the official login page, enter your email and password, and click Sign In. If you’ve done that and still can’t access your dashboard, the guide below explains every possible snag and how to fix it.
Key Takeaways
- Use the official URL https://app.gohighlevel.com/; any other domain is likely a phishing site.
- Two‑factor authentication (2FA) is optional but strongly recommended for agency accounts.
- Common login failures stem from password typos, browser cache, or a disabled account.
- Resetting a password requires access to the email tied to the account.
- If you’re locked out after multiple attempts, contact HighLevel support via the community portal.

What URL Should I Use for a go high level login?
The only legitimate entry point is app.gohighlevel.com. The platform occasionally redirects to a sub‑domain for single‑sign‑on (SSO) partners, but the base URL never changes. Bookmark it and avoid shortcuts sent in email newsletters – phishers often mimic the look of the login screen.
How Do I Enter My Credentials Correctly?
HighLevel accepts the email address you used when you signed up and a password that meets these rules: at least eight characters, a mix of upper‑ and lower‑case letters, a number, and a special character. The password field masks characters, so double‑check for accidental spaces before or after the string.
Tip: copy‑paste passwords from a password manager, but make sure the manager doesn’t add a trailing space. Many users report a “incorrect password” error that disappears once they re‑type the password manually.
What If I Forget My Password?
Click the “Forgot password?” link beneath the sign‑in button. HighLevel will email a reset link to the address on file. The link expires after 60 minutes, so act promptly. If you no longer have access to that email, you’ll need to contact support with proof of ownership – usually a screenshot of a recent invoice or the agency’s legal name.
How to Enable Two‑Factor Authentication (2FA) for Extra Security
After you log in, go to Settings → Security. Choose an authenticator app (Google Authenticator, Authy, etc.), scan the QR code, and enter the six‑digit code generated by the app. HighLevel stores the secret key locally, so you won’t lose access if you change phones – just re‑scan the QR code from the same Settings page.
Enabling 2FA reduces the risk of credential stuffing attacks, which are common against SaaS platforms that host many agency accounts.
Why Does My Browser Keep Redirecting Me Back to the Login Page?
This usually means the session cookie was blocked. Check that your browser allows third‑party cookies for the domain app.gohighlevel.com. Also clear the cache and cookies for that site; stale session data can cause an infinite loop.
Incognito or private‑browsing modes often bypass saved cookies, so try logging in there to see if the problem persists. If it works in incognito, the issue is almost certainly a cached cookie.
What Are the Most Common Login Errors and How to Fix Them?
| Error Message | Likely Cause | Fix |
|---|---|---|
| Incorrect email or password | Typo, outdated password, or account disabled | Reset password; verify email spelling; contact support if disabled |
| Account not verified | New account awaiting email confirmation | Find the verification email (check spam) and click the link |
| Too many attempts – try later | Brute‑force protection throttling | Wait 15 minutes, then try again; enable 2FA to avoid future throttles |
| Browser not supported | Outdated Chrome/Firefox version | Update browser to the latest version |
How to Troubleshoot a Locked Account After Multiple Failed Logins
HighLevel locks an account after ten consecutive failed attempts. The lock lasts 30 minutes, but you can accelerate the process by resetting the password. The reset email also clears the lock flag.
If you’re an agency manager and need to unlock a team member’s account immediately, use the “Admin → Users” panel (if you have admin rights) to toggle the “Active” switch off and on. This forces a session refresh and removes the lock.
Can I Use Single Sign‑On (SSO) Instead of a Password?
HighLevel supports SAML 2.0 for enterprise customers. To enable SSO, an admin must configure the identity provider (Okta, Azure AD, etc.) in Settings → Integrations. Once set, the login page shows a “Sign in with [Provider]” button, and users are redirected to the IdP for authentication.
If you’re on a standard agency plan, SSO isn’t available out of the box; you’d need to upgrade to a custom enterprise contract.
What Should I Do If I Suspect My Account Was Compromised?
Immediately log out of all devices via Settings → Security → Log out of all sessions. Then change your password, enable 2FA, and review the “Login History” table for unfamiliar IP addresses. If you see logins from locations you don’t recognize, contact HighLevel support and consider revoking API keys that may have been exposed.
How Does the go high level login Fit Into an Agency Workflow?
Most agencies use the login as the first step before accessing pipelines, funnel builders, and client dashboards. A smooth login experience reduces friction for sales teams that need to pull up client reports on the fly.
Because the platform stores client data, compliance teams often require a documented login process. The steps above give you a repeatable checklist for onboarding new staff.

Where Can I Find Official Help If I’m Still Stuck?
The HighLevel community forum hosts a dedicated “Login Issues” thread. Visit the official community login page and search for your error message. If nothing matches, open a new ticket; support typically replies within 24 hours.
For a quick internal reference, check our SimpCity login guide, which covers similar SaaS login flows and shares troubleshooting patterns that also apply to HighLevel.
What to Do Next
- Bookmark the official login URL and enable 2FA today.
- Run through the checklist above on a test account to verify each step works.
- Document the process in your agency’s SOP and share it with new hires.
What Browser Settings Can Prevent Login Issues?
Most login hiccups stem from a browser that’s not set up for the platform. Before you start troubleshooting credentials, check these three settings.
1. Cookies and Site Data
go high level relies on cookies to keep you signed in after the first successful authentication. If your browser blocks third‑party cookies or clears site data on exit, you’ll be bounced back to the login screen.
- Chrome / Edge: Settings → Privacy and security → Cookies and other site data → Allow all cookies or “Allow cookies from sites you visit”.
- Firefox: Preferences → Privacy & Security → Cookies and Site Data → Standard (or Custom with “Cookies” set to “Accepted”).
- Safari: Preferences → Privacy → Uncheck “Prevent cross‑site tracking”.
2. Pop‑up and Redirect Blocking
The platform sometimes opens a small pop‑up for two‑factor verification or for password‑reset flows. A strict pop‑up blocker will stop that window, leaving the main page thinking the login never finished.
- Disable the blocker for
app.gohighlevel.comor add the domain to the “allowed” list. - If you use an extension like uBlock Origin, whitelist the domain under “My filters”.
3. Cached Data and Stale Sessions
Old cache entries can cause the browser to serve an outdated login page that no longer matches the server’s expectations. A quick cache clear often resolves mysterious redirects.
- Press Ctrl+Shift+Del (Windows) or Cmd+Shift+Delete (Mac) and clear “Cached images and files”.
- Restart the browser after clearing to ensure a fresh session.
By confirming these three settings, you eliminate the most common non‑credential‑related roadblocks before moving on to password or 2FA problems.
How to Log In Using a Temporary Access Link (Guest Mode)
Agencies sometimes need to give a client a quick look at a funnel or campaign without creating a full user account. go high level offers a “temporary access link” that expires after a set period.
Step‑by‑Step Creation
- Navigate to Settings → Team & Permissions in your agency dashboard.
- Click Generate Guest Link next to the funnel or pipeline you want to share.
- Choose an expiration: 24 hours, 7 days, or a custom date.
- Copy the URL and send it to the client via email or chat.
How the Guest Link Works
The link contains a signed token that authenticates the user for that specific resource only. When the client clicks it, they land on a stripped‑down version of the dashboard that shows the selected funnel, plus a “Request Access” button if they need more.
Common Mistakes and How to Avoid Them
- Using the wrong resource. The link is tied to the exact funnel you selected. Double‑check the funnel name before generating.
- Setting an overly long expiration. Longer windows increase security risk. Stick to the shortest practical period.
- Forgetting to revoke. If a client should no longer see the link, go back to the same settings page and click “Revoke”. The token becomes invalid instantly.
When Guest Mode Isn’t Suitable
If the client needs to edit contacts, send messages, or view analytics across multiple funnels, a full user account with role‑based permissions is safer. Guest mode is best for one‑off reviews or proof‑of‑concept demos.
Login Method Comparison: Password vs SSO vs Magic Link
Choosing the right authentication method depends on how your agency balances security, convenience, and client onboarding speed. Below is a quick side‑by‑side look.
| Method | Security | Setup Time | Best For |
|---|---|---|---|
| Password | Standard – relies on password strength and optional 2FA. | Immediate – just create a password. | Small teams or users who already have a corporate password policy. |
| Single Sign‑On (SSO) | High – delegates authentication to an identity provider (Okta, Azure AD, etc.). | Moderate – requires SSO configuration in both IdP and go high level. | Agencies with many staff members or clients that already use SSO. |
| Magic Link | Medium – link expires quickly and is sent to a verified email. | Low – no password to remember, just enable the feature. | Quick client demos or temporary collaborators. |
In practice, most agencies start with password + 2FA for internal users, enable SSO for larger staff, and reserve magic links for short‑term guest access. Switching between methods later is possible, but it requires re‑assigning roles and notifying users.
Decision Rule
If you already have an identity provider that your team trusts, enable SSO and disable password login to reduce phishing risk. If you’re a solo agency or just onboarding a client for a single project, the magic link is the fastest route, provided you verify the email address first.
Remember to review the chosen method quarterly. Security standards evolve, and a method that felt sufficient a year ago might need tightening today.
Frequently Asked Questions
Can I log in to HighLevel from a mobile device?
Yes. HighLevel offers native iOS and Android apps. The mobile login uses the same email/password combo, and you can enable 2FA within the app’s Settings.
Is there a way to bypass the password reset if I don’t receive the email?
If the reset email isn’t arriving, first whitelist @gohighlevel.com in your email client. If it still doesn’t show up, contact support and provide your agency’s subscription ID for verification.
Do third‑party password managers work with HighLevel?
They work fine as long as the manager fills the password field without extra spaces. Test with a simple site first to confirm the autofill behavior.